
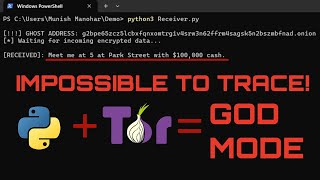



Ghost Messenger is a high-security, peer-to-peer (P2P) communication framework designed for total anonymity. By leveraging AES-256-GCM authenticated encryption and the Tor (Onion Router) network, Ghost Messenger ensures that both the content and the metadata of your communications remain invisible to ISPs, governments, and third-party attackers.
Unlike traditional messaging apps (Signal, Telegram, WhatsApp), Ghost Messenger has zero central servers.
- Onion Services: The receiver generates an ephemeral
.onionaddress that exists only in RAM. - Triple-Layer Routing: Messages are bounced through three different global nodes before reaching the destination.
- Cryptographic Integrity: Every packet is encrypted with AES-256-GCM, ensuring that if even a single bit is altered in transit, the packet is dropped.
- Zero-Trace: No logs, no history, and no forensic trail.
Ensure you are running Kali Linux or a similar Unix-based environment with the Tor service active.
# Install system-level dependencies
sudo apt update && sudo apt install tor -y

# Install Python dependencies
pip3 install cryptography stem PySocksTo allow the Python controller to interface with the Tor circuit, modify your torrc file:
sudo nano /etc/tor/torrc
Add or uncomment the following lines:
ControlPort 9051
CookieAuthentication 1
CookieAuthFileGroupReadable 1
Restart the service and update permissions:
sudo service tor restart
sudo usermod -a -G debian-tor $USERGhost Messenger operates in a Receiver-First architecture.
On the receiving machine, run the listener. This will generate your unique, one-time-use .onion ghost address.
python3 receiver.pyWait for the [!!!] GHOST ADDRESS to appear. Share this address with the sender over a secure channel.
On the sending machine, run the sender and input the ghost address provided by the receiver.
python3 sender.pyGhost Messenger is an Ethical Hacking and Privacy Research tool. It is designed for educational purposes and to demonstrate secure communication protocols. Unauthorized use of this tool for malicious activities is strictly prohibited. The developer is not responsible for any misuse.
Developed for research purposes in the 2026 Cybersecurity Landscape.